
Cybersecurity compliance software helps organizations manage security controls, policies, evidence, risk assessments, and regulatory requirements in one system. It supports continuous monitoring, reporting, audit preparation, and remediation tracking across cybersecurity and compliance operations.

Cybersecurity Compliance Software & Risk Management Solutions to Protect Your Business
We build cybersecurity compliance and risk management software for monitoring, access control, threat detection, vendor risk, and recovery.
Trusted By
Key Takeaways
Why Organizations Choose Chetu for Cybersecurity & Compliance
We resolve complicated compliance and cybersecurity demands with customized solutions that fit perfectly into your existing environment.
Connected Security & Compliance Systems
Administer identity management, compliance monitoring, risk information, vendor evaluations, security measures, and reports through unified workflows instead of unconnected systems.
Risk-Based Security Management
Aid security teams in determining the priority of issues according to accepted business and security standards by employing asset data, vulnerability details, threat intelligence, and adjustable risk evaluation.
Continuous Compliance Monitoring
Streamline routine compliance activities, handle documentation with report generation for obligations such as GDPR and HIPAA.
Custom Cybersecurity Development
Develop new cybersecurity applications, update existing systems, or connect security and compliance tools across your enterprise technology stack.
Watch
Connect Security, Compliance, and Risk in One Environment
Security and compliance teams often use separate tools for identity, vulnerabilities, policies, vendors, reporting, and recovery.
Chetu builds cybersecurity software that brings these functions together through custom applications, integrations, automation, dashboards, and security workflows configured for your existing infrastructure.
We help teams manage cybersecurity and risk within a connected system from IAM and penetration testing to compliance management.
SEE WHAT WE CAN DO FOR YOU
Free Download
Building a Resilient Compliance Program: From Risk to Regulation
Learn how organizations can organize cybersecurity risk management, compliance monitoring, identity controls, vendor oversight, and recovery planning within one connected compliance program.
What We Do
Cybersecurity Compliance & Risk Management Solutions
Build cybersecurity and compliance solutions tailored to the unique systems, risks, regulations, and operational demands of your organization.
Cybersecurity Compliance Software
Manage controls tracking, documentation, policies, regulatory obligations, and compliance reporting with software configured around your internal procedures.
Automated compliance monitoring can minimize repetitive tracking efforts while providing security and compliance teams with an updated view of controls, findings, and the status of remediation efforts.
Identity & Access Management Solutions
Access control, authentication, and identity management allow you to manage user rights over apps, systems, and sensitive data.
We implement IAM functionality such as access control, multi-factor authentication, single sign-on, lifecycle user management, periodic access reviews, and approval requests.
Cloud Security & Penetration Testing
Check applications, infrastructure, and clouds for faults, misconfigurations, and other vulnerabilities.
We perform security device management, recommend countermeasures, identify vulnerabilities, perform penetration tests, manage vulnerabilities, and follow-up on repair activities.
Threat Intelligence & Cybersecurity Risk Management
Using risk factors, regulatory requirements, asset information, vulnerability detection, and threat intelligence, develop a risk management system.
Security teams may identify where vulnerability exists and which problems need care throughout continuous security operations thanks to custom dashboards and remediation workflows.
Data Protection, Backup & Disaster Recovery
Build processes for protecting, backing up, restoring, and recovering critical information and systems.
Our data protection solutions support encryption, automated backup, recovery workflows, defined RTO and RPO requirements and business continuity management.
Vendor Risk & Enterprise Compliance
Go beyond your internal systems to oversee cybersecurity and compliance requirements.
A solution that manages vendor risks might combine recurring assessments, discoveries, documents, remedies, policy needs, and third-party evaluations across vendors, business units, and departments.
Let's Fix What Is Creating Security & Compliance Risks
Book a 20-minute consultation with our cybersecurity team. We will review your current systems, compliance requirements and development needs to identify how custom software, integration, or automation may help.
Discuss your current cybersecurity and compliance requirements
Identify software, workflow, and integration gaps
Define a practical development approach based on your environment
Deep Platform Expertise
Cybersecurity & Compliance Solutions Designed Around Your Environment
Cybersecurity operations involve regulations, users, systems, vendors, infrastructure, risk data, and recovery processes. These functions often sit across different applications and teams.
Chetu develops connected security and compliance solutions that help organizations manage these activities through software designed for their existing technology environment and operating requirements.
HIPAA & GDPR Compliance Software
VOrganizations that are subject to regulations concerning data privacy and healthcare need a uniform method for handling regulatory needs, reporting, evidence, and policies. Our software for HIPAA and GDPR compliance helps teams track control status, manage documents, automate compliance processes, and get ready for audits using a single system.
- Automated Compliance Monitoring - Track compliance controls continuously and identify gaps that require review or remediation.
- Map policies and controls - Link security procedures and internal regulations to the appropriate HIPAA and GDPR standards.
- Reporting & Compliance Dashboards - Give compliance teams access to supporting evidence, control status, and unanswered issues.
- Data Subject Access Request Management - Manage GDPR-related access, correction, deletion, and information requests through structured workflows.
- Regulatory Requirement Management - Maintain compliance workflows and control mappings as applicable requirements change.
Identity & Access Management Solutions (IAM Solutions)
VExcessive, outdated, or poorly administered access rights could put sensitive data and systems at risk. Organizations can regulate who has access, what resources they can access, and how rights vary through user connections with the aid of our identity and access management solutions.
- Role-Based Access Control - Assign access based on defined roles, responsibilities, and permission requirements.
- Multi-Factor Authentication - Increase the number of layers of identity validation for users accessing secure systems.
- Single Sign-On Integration - Unify user authentication for multiple services and applications.
- Identity Governance & Lifecycle Management - Oversee provisioning, access changes, reviews, and account deactivation.
- Least-Privilege Access Controls - Restrict access to the least-privilege level necessary for each user, role, or business activity.
Cybersecurity Risk Management & Threat Intelligence
VAlerts, threat intelligence data, security findings, and compliance issues may be shared across security teams through various platforms. Our cyber risk management solutions enable teams to score prioritize assign, and monitor security threats utilizing defined workflows and shared data.
- Continuous Vulnerability Monitoring - Collect and analyze vulnerability data from infrastructure and linked applications.
- Risk Scoring & Prioritization - Rank risks according to severity, exposure, business impact, and specified organizational standards.
- AI-Powered Threat Detection - To spot patterns and events that need to be looked at, use AI-assisted analysis of security data.
- Cyber Risk Dashboards - Provide security and leadership teams with visibility into risks, remediation status, and exposure.
- Automated Risk Alerts - Trigger notifications and workflows when security or compliance thresholds are reached.
Penetration Testing & Cloud Security Services
VMonitoring on a regular basis may not detect security flaws in settings or difficulties with applications and cloud environments. Our cloud security and penetration testing services enable businesses to assess these configurations, record findings, and administer remediation tasks.
- Manual & Automated Penetration Testing - Conduct manual and automated penetration testing to identify vulnerabilities in applications, systems, and infrastructure that may be exploited.
- Cloud Configuration Assessments - Examine cloud environments for configuration flaws, access dangers, and security gaps.
- Vulnerability Remediation Workflows - Track, assign, prioritize, and verify remediation activities.
- Security Device Management - Manage security controls and monitoring across network settings and endpoints.
- Security Assessment Reporting - Document your discoveries, their severity, the systems that are affected, and the corrective actions.
Backup & Disaster Recovery, Data Protection
VDisruptions such as cyber-attacks, infrastructure outages, and other incidents might prevent access to vital systems and information. Our solutions for disaster recovery and data protection assist businesses in protecting data, automating backups, defining recovery needs, and preparing systems for restoration.
- Backup and Recovery of Data - Automate backup procedures and enable regulated restoration of important data.
- Encryption at Rest and Transit - protects sensitive information during storage and transfer.
- Plan for Disaster Recovery - Establish restoration dependencies, duties, priorities, and recovery procedures.
- RTO & RPO Management - Establish recovery processes in accordance with the needed recovery time and recovery point targets.
- Business Continuity Management - Support continuity planning, readiness for operational disruptions, and recovery testing.
Vendor Risk & Enterprise Compliance Management
VThird-party vendors and distributed business operations can introduce security and compliance risks that are difficult to manage through separate documents and spreadsheets. Our vendor risk and enterprise compliance solutions centralize assessments, findings, policies, remediation tasks, and compliance records.
- Vendor Risk Assessments - Evaluate vendors against defined cybersecurity, compliance, and operational requirements.
- Third-Party Remediation Tracking - Record findings, assign corrective actions, and track unresolved vendor risks.
- Patch Management Workflows - Track software and system updates associated with vulnerabilities and security requirements.
- Compliance Policy Lifecycle Management - Manage policy creation, approval, review, revision, and documentation.
- Centralized Enterprise Compliance - Consolidate compliance activities across departments, business units, and regions.
Business Outcomes
What Connected Cybersecurity & Compliance Software Can Improve
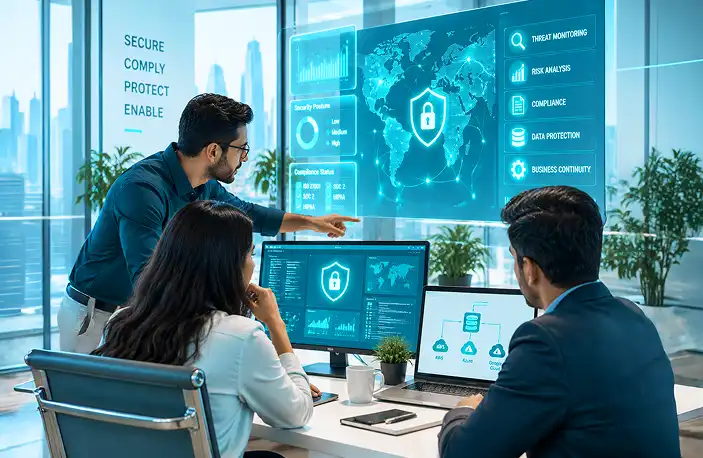
- Reduced Risk Exposure
Teams may determine which security vulnerabilities need attention and track actions through resolution thanks to centralized vulnerability data, threat intelligence, risk scoring, and remediation processes.
- Audit-Ready Compliance
Teams have continuous access to control status, evidence, rules, outstanding activities, and reporting data required for internal and external compliance evaluations through automated compliance monitoring.
- Business Continuity
In the case of a disturbance, continuity management, disaster recovery, and backup skills assist organizations in establishing essential data and systems should be recovered.
Our Cybersecurity Compliance Development Process
From Ongoing Risk Management to Assessment
Step 01: Risk Analysis
and Assessment
Examine the systems, security controls, compliance requirements, vulnerabilities, procedures, data flows, and known operational hazards that are currently in place.
The evaluation identifies security, software, integration, and process gaps that must be filled.
Step 02: Security
Architecture and Compliance
Explain how monitoring, identity management, encryption, risk data, reporting tools, compliance workflows, and existing systems will collaborate.
Based on your infrastructure, security policies, technological dependencies, and regulatory needs, the architecture was created.
Step 03: Identity
& Access Configuration
Configure authentication, user roles, permissions, access policies, identity governance, and workflows for approval.
Access controls can also relate to compliance monitoring and security reporting systems.
Step 04: Pilot
& Penetration Testing
Deploy selected functionality within a controlled scope and test applications, integrations, and infrastructure for security weaknesses.
Identified issues can be documented, prioritized, assigned, and retested after remediation.
Step 05: Scaling
& Automated Monitoring
Extend approved functionality across the required systems, teams, departments, or business units.
Configure automated compliance monitoring, security alerts, risk scoring, reporting, and workflow automation according to operating requirements.
Step 06: Ongoing Risk, Vendor
& Compliance Management
Support recurring risk assessments, vendor reviews, access reviews, patch management, compliance updates, monitoring, and remediation through structured workflows.
Cybersecurity Expertise
How Cybersecurity Compliance Software Supports Risk Management
Managing cybersecurity risk involves more than collecting alerts. Security teams need to understand which systems are affected, how serious the exposure is, which compliance requirements apply, who owns remediation, and whether corrective action has been completed.
Cybersecurity compliance software can connect to these activities. Automated compliance monitoring can track controls and support evidence. Identity integrations can provide access information. Threat detection systems can send findings into risk workflows. Penetration testing results can be assigned for remediation. Vendor risk management software can track third-party assessments and corrective actions.
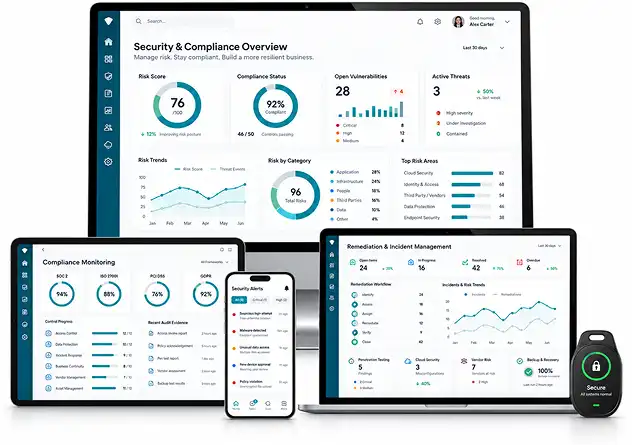
By connecting this information, security and compliance teams can work from a shared view of risk instead of maintaining separate records across multiple systems.
Explore Our Cybersecurity Capabilities
- HIPAA Compliance Software
- GDPR Compliance Software
- Identity & Access Management Solutions
- Cybersecurity Risk Management
- Penetration Testing Services
- Cloud Security Services
- Data Backup & Recovery Services
- Vendor Risk Management Software
Industries
Cybersecurity & Compliance Solutions Across Regulated Industries
Finance & Banking Develop systems for regulatory compliance, transaction monitoring, fraud detection, identity management, access control, data protection, and cyber risk management.
Healthcare Support HIPAA compliance, patient data protection, access governance, secure healthcare systems, backup processes, recovery planning, and compliance reporting.
Retail & eCommerce Protect customer and payment information through access controls, fraud prevention, data protection, security monitoring, vendor oversight, and compliance workflows.
Manufacturing Connect IT and operational security processes with patch management, vendor risk management, business continuity planning, access controls, and centralized security reporting.
Government Support compliance reporting, identity management, threat detection, security device management, risk tracking, and audit preparation across public sector systems.
Professional Services Protect client and business information through GDPR compliance software, identity governance, secure document workflows, data protection, and controlled system access.
Custom Cybersecurity Solutions
Hire Cybersecurity Software Developers for Custom Compliance Solutions
Security and compliance software has to work with existing infrastructure, security policies, regulatory requirements, and business processes. Generic tools do not always provide the workflows, integrations, reporting, or controls an organization requires.
Chetu's cybersecurity software developers build, integrate, modernize, and maintain custom security and compliance applications based on those requirements.
Our Cybersecurity Software Development Expertise
- Security Compliance Software Development
- Cybersecurity Application Development
- AI-Powered Cybersecurity Solutions
- Compliance Management Software Development
- IAM & Identity Governance Development
- Threat Detection & Risk Scoring Systems
- Cloud Security Tool Development
- Regulatory Compliance Automation
- Vendor & Third-Party Risk Platforms
- Disaster Recovery & Backup System Integration
AI-Assisted Development
Our AI-Assisted Development Model
Our developers remain responsible for the architecture, code, testing, security decisions, and finished software we deliver.
Within approved projects, our development teams can use AI-assisted tools across parts of the software development lifecycle to support activities such as coding, testing, debugging, documentation, and development analysis. These tools are used within the development process. They do not replace engineering ownership or turn project delivery into automated copy-and-paste development.
The development approach is selected according to the project's technical, security, compliance, and governance requirements.
Developer-Led Software Delivery
Chetu developers design the architecture, make technical decisions, review generated outputs, write and validate code, test integrations, and remain accountable for the delivered solution.
AI-Assisted Development Workflows
AI-assisted tools can support defined development tasks where they provide a practical efficiency benefit, while engineering review remains part of the process.
Security, Privacy & IP Considerations
AI-assisted development can be incorporated according to project requirements, data handling policies, development controls, and applicable governance standards.
Organizations with policies that restrict AI-assisted development can use a traditional development approach where required.
AI Efficiency 10–40% Efficiency Gains 10–40% efficiency gains from AI-Assisted development.
Gains vary by project, and we're transparent about where AI adds value and where it doesn't.
"Either way, we own the outcome."
The Numbers
Numbers That Get Security and Compliance Decision-Makers Excited
Board decks, procurement reviews, and security leadership teams all ask the same question: "Who's done this before?" And the answer is
20+
Cybersecurity & Compliance Platforms Supported
60+
Compliance & Risk Use Cases Accelerated
HIPAA & GDPR
Aligned Security-First & Delivery Framework
45 Days
Compliance-Ready Software Delivered
Proof
Chetu in cybersecurity & compliance: success stories
Hear What Our Clients Have to Say
Build Your Cybersecurity Compliance Solution
Your cybersecurity environment may already include identity systems, cloud platforms, security tools, compliance processes, vendor records, monitoring applications, and recovery infrastructure.
The next step is identifying where those systems need better integration, where workflows can be automated, and where custom software is required.
Book a free 20-minute consultation to discuss your current cybersecurity and compliance environment with our team.
Frequently Asked Questions About Cybersecurity Compliance Software
Automated compliance monitoring tracks controls, identifies gaps, and reduces repetitive compliance checks. It gives security and compliance teams better visibility into current status, outstanding issues, supporting evidence, and remediation activities between formal audits.
Yes. Custom compliance software can support HIPAA and GDPR requirements through policy mapping, control tracking, documentation, reporting, access management, and structured workflows. The exact configuration depends on the organization’s systems, processes, and regulatory responsibilities.
Identity and access management controls who can access systems, applications, and sensitive data. Features such as role-based access control, multi-factor authentication, single sign-on, and identity governance help reduce unauthorized access and manage permissions more consistently.
Cybersecurity risk management software combines vulnerability findings, threat intelligence, asset information, and defined risk criteria. It helps security teams score risks, prioritize remediation, assign ownership, track progress, and maintain visibility into security exposure.
Penetration testing identifies exploitable vulnerabilities across applications, infrastructure, and cloud environments. Findings can be documented, prioritized, assigned for remediation, and retested, helping organizations address security weaknesses and maintain evidence for compliance and risk management processes.
Vendor risk management software centralizes third-party assessments, documentation, findings, remediation tasks, and recurring reviews. It helps organizations track external security risks, maintain vendor oversight, and connect third-party risk information with broader compliance and cybersecurity processes.
Yes. Chetu develops custom applications, APIs, integrations, dashboards, and automation that connect with existing identity, cloud, compliance, risk, and security systems. The goal is to improve coordination without requiring organizations to replace their full technology environment.
Our
Portfolio
A showcase of our diverse solutions, services and industry expertise.